Rate this post

Linux Foundation New 2026 CKA Sample Questions Reliable CKA Test Engine

Feel Linux Foundation CKA Dumps PDF Will likely be The best Option

Q49. Configure the kubelet systemd-managed service, on the nodelabelled withname=wk8s-node-1, tolaunch a pod containing a singlecontainer of Image automatically. Any spec filesrequired should be placed in the/etc/kubernetes/manifests You canssh to theappropriate node using:
[student@node-1] $ sshwk8s-node-1
You can assume elevatedprivileges on the node with thefollowing command:
[student@wk8s-node-1] $ |sudo -i

Q50. Your team has deployed a containerized application on Kubernetes. You have configured a deployment with a replica count of 3 pods. The application uses a resource-intensive process that consumes a significant amount of CPU resources. You are experiencing performance issues and suspect that the pods are competing for resources. Explain how you can use resource quotas and limits to address this problem.

Q51. Score: 13%

Task
A Kubernetes worker node, named wk8s-node-0 is in state NotReady. Investigate why this is the case, and perform any appropriate steps to bring the node to a Ready state, ensuring that any changes are made permanent.

Q52. Get list of all the pods showing name and namespace with a jsonpath expression.

Q53. Check the rollout history and make sure everything is ok after the update


Q54. From the pod label name=cpu-utilizer, find pods running high CPU workloads and write the name of the pod consuming most CPU to the file /opt/KUTR00102/KUTR00102.txt (which already exists).

Q55. Create a snapshot of the etcd instance running at https://127.0.0.1:2379, saving the snapshot to the file path /srv/data/etcd-snapshot.db.
The following TLS certificates/key are supplied for connecting to the server with etcdctl:
CA certificate: /opt/KUCM00302/ca.crt
Client certificate: /opt/KUCM00302/etcd-client.crt
Client key: Topt/KUCM00302/etcd-client.key

Q56. You must connect to the correct host.
Failure to do so may result in a zero score.
[candidate@base] $ ssh Cka000054
Context:
Your cluster ‘s CNI has failed a security audit. It has been removed. You must install a new CNI that can enforce network policies.
Task
Install and set up a Container Network Interface (CNI ) that meets these requirements:
Pick and install one of these CNI options:
Flannel version 0.26.1
Manifest:
https://github.com/flannel-io/flannel/releases/download/v0.26.1/kube-flannel.yml
Calico version 3.28.2
Manifest:
https://raw.githubusercontent.com/project calico/calico/v3.28.2/manifests/tigera-operator.yaml

Q57. create a pod in a specific node (node1) by placing the pod definition file in a particular folder “/etc/kubernetes/manifests”.


Q58. You have a StatefulSet named ‘database-statefulset’ that runs a database service. The database requires persistent data storage. You are experiencing a problem where the database pods are crashing repeatedly, and the database data is getting lost. You suspect that there is an issue with the persistent volume claim (PVC) used by the StatefulSet. How would you troubleshoot and potentially fix this problem?

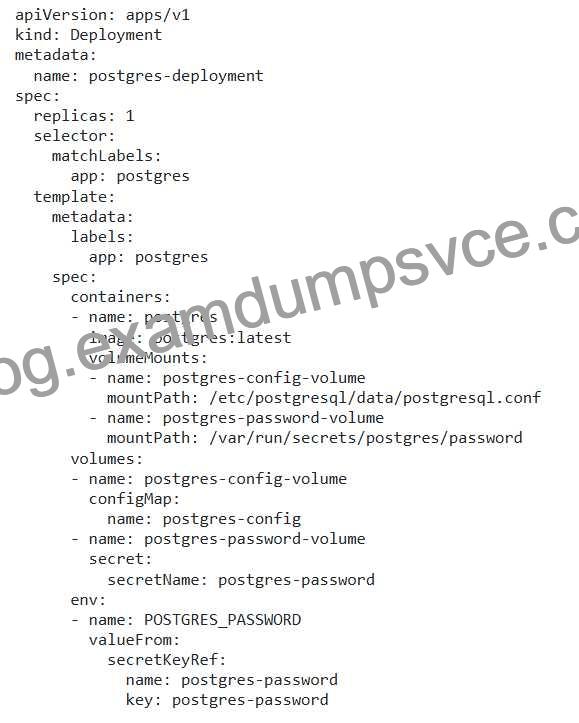
Q59. You have a Deployment named ‘postgres-deployment’ running a PostgreSQL database server. You need to configure the PostgreSQL server with a specific configuration file stored in a ConfigMap named postgres-config’. The configuration file includes sensitive information like the PostgreSQL superuser password. How can you securely store and mount this sensitive information without compromising security?

Q60. Create a pod that echo “hello world” and then exists. Have the pod deleted automatically when it’s completed

Q61. You have a Deployment for a web application named ‘web-app-deployment’ that uses an image named ‘web-app:vl .0’. You want to implement a rolling update to upgrade the deployment to a new version, ‘web-app:v2.0’, but only allow a maximum of 2 pods to be unavailable at any time during the update. How would you achieve this using Kubernetes?

Q62. List all the events sorted by timestamp and put them into file.log and verify


Q63. Create a pod as follows:
* Name:non-persistent-redis
* container Image:redis
* Volume with name:cache-control
* Mount path:/data/redis
The pod should launch in thestagingnamespace and the volumemust notbe persistent.

Q64. You are tasked with securing a Kubernetes cluster by implementing RBAC. Your cluster has two namespaces: ‘dev’ and ‘prod’. You need to create a role that allows users in the ‘dev’ namespace to create, delete, and list deployments, but only read-only access to deployments in the ‘prod’ namespace. Additionally, these users should have access to create and manage ConfigMaps within both namespaces.
Create the necessary RBAC resources (Role, RoleBinding) to implement this access control policy.


Use Valid New CKA Test Notes & CKA Valid Exam Guide: https://www.examdumpsvce.com/CKA-valid-exam-dumps.html


Related Links: myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below